FATCA petition in the Committee on Petitions | Commission Reply of 15 February 2022

In the Committee on Petitions (PETI) of the European Parliament complaints by three victims of the unlawful extraterritorial legislation of the U.S., FATCA, are dealt with.

PETI published a notice to members with a summary of the complaints and the information provided by the European Commission, the latest is of 15 February 2022 (page 5-7):

6. Commission reply (REV III), received on 15 February 2022
Petitions 1088/2016, 1470/2020 and 0323/2021

Following its meeting on 10 November 2020, the Committee on Petitions requested an updated reply, especially in view of the recent United States (US) elections and new US administration. The Commission is also providing an update in view of the Committee on Petitions meeting of 2 September 2021.

On 8 December 2020, the German Presidency of the Council of the EU wrote a letter to the US administration (Internal Revenue Service (IRS)) on the Foreign Account Tax Compliance Act (FATCA).

This letter (which is publicly accessible) can be found under the following link: https://data.consilium.europa.eu/doc/document/ST-13977-2020-INIT/en/pdf

In its letter, the German Presidency stressed that, in spite of the relief measures taken thus far by the US authorities as regards individuals with US nationality wishing to relinquish their US nationality (measures previously reported by the Commission services to the Committee on Petitions), EU citizens with US nationality are still experiencing concrete difficulties (e.g. complex procedures and high renunciation fees – around 2 300 US dollars). Contacts between the EU Presidency and the US administration continued under the Portuguese Presidency. A meeting between the Presidency and the US IRS took place on 25 March 2021.

On 16 September 2021, the US IRS replied to the letter referred to above, indicating its willingness to better understand the circumstances under which Foreign Financial Institutions (FFIs) are not able to report a taxpayer identification number (TIN). The IRS indicated that such information would allow the US administration to give further consideration as to whether additional measures could be taken to encourage TIN reporting, and whether additional relief could be provided to FFIs or US taxpayers resident abroad.

The Commission’s observations

Contacts between EU institutions and the US administration on FATCA are ongoing. FATCA was, in particular, discussed by the Commission services with high-level representatives of the US administration at the EU-US Joint Regulatory Forum on 24-25 March 2021 and again on 29-30 September 2021 at which the US administration stressed its willingness to cooperate with the Commission to find mutually acceptable solutions to the problems presented by the Commission services. The Commission services had in particular highlighted the impact of FATCA on the accessibility, by ‘accidental Americans,’ to basic financial services such as a bank account. The Commission services will now follow up on the US administration’s invitation to cooperate.

The US IRS updated in May 2021 its frequently asked questions (FAQs) on general issues of FATCA. The updated FAQs provide information for Model 1 FFIs that are required, but have not been able to obtain and exchange the US TIN for each specified US person that is an account holder or a controlling person of a non-US entity.

The updated FAQs, dated 13 May 2021, include a new question (Q6), in the Reporting subsection of the FAQs. Q6 lists a series of codes that may be used by a reporting Model 1 FFI to populate the TIN field where the TIN has not been obtained in specified scenarios. The use of these codes is not mandatory but is expected to help the IRS better understand the facts and circumstances behind the missing TINs, and therefore assess the compliance of the FFI with its reporting obligations.

When one of the codes is used, the IRS system will generate an error notification to indicate that the entry is invalid. The error notification will provide 120 days to correct the issue by providing the TIN. If the TIN is not provided within 120 days, the IRS will evaluate the data received and determine through a consideration of facts and circumstances whether there is significant non-compliance. Such facts and circumstances include:

– reasons why the TIN could not be obtained;
– whether the FFI has adequate procedures in place to obtain TIN; and
– efforts made by the FFI to obtain TINs.

These changes go in the direction expected by the Commission regarding ways to address the difficulties in reporting the US TIN by the FFIs.

As regards data protection, the European Data Protection Board (EDPB) issued a statement [1] on 13 April 2021 in which it recalls the principles enshrined in Article 96 of the General Data Protection Regulation (GDPR) [2] and Article 61 of the Law Enforcement Directive (LED) [3], according to which existing international agreements involving international transfers of personal data which comply with Union law as applicable prior to the entry into force of the Regulation or Directive remain in force until amended, replaced or revoked.

The EDPB considers that, in order to ensure that the level of protection under the GDPR and the LED is not undermined when personal data is transferred outside the Union, consideration should be given to the aim of bringing these agreements in line with the GDPR and LED where this is not yet the case.

On that basis, in the same statement, the EDPB invited Member States to assess and, where necessary, review their international agreements that involve international transfers of personal data, such as those relating to taxation (e.g. to the automatic exchange of personal data for tax purposes) to determine whether further alignment with current EU legislation, case law and EDPB guidance might be needed.

As also indicated in the EDPB statement, national data protection authorities, as the enforcers of the data protection rules, have an important role in providing assistance and advice to Member State authorities in this context.

Conclusion

The Commission services are in frequent contact with the Member States, the EU Presidency and the EDPB on this file. Contacts are also held with European banks to ensure access to a basic bank account by, in particular, EU citizens also possessing US nationality. The Commission views this file with utmost importance and will continue to inform the Committee on Petitions of any progress made, following in particular the discussions held at the Committee on Petitions meeting of 2 September 2021.


[1] Available at:

https://edpb.europa.eu/system/files/2021-04/edpb_statement042021_international_agreements_including_transfers_en.pdf .

[2] Regulation (EU) 2016/679 of the European Parliament and of the Council of 27 April 2016 on the protection of natural persons with regard to the processing of personal data and on the free movement of such data, and repealing Directive 95/46/EC (General Data Protection Regulation) (Text with EEA relevance), OJ L 119, 4.5.2016, p. 1–88.

[3] Directive (EU) 2016/680 of the European Parliament and of the Council of 27 April 2016 on the protection of natural persons with regard to the processing of personal data by competent authorities for the purposes of the prevention, investigation, detection or prosecution of criminal offences or the execution of criminal penalties, and on the free movement of such data, and repealing Council Framework Decision 2008/977/JHA, OJ L 119, 4.5.2016, p. 89–131.
Geplaatst in Bankrekening krijgen en behouden, Belastingrecht, English - posts in English on this blog, Europa, Financieel recht, onder meer Wft, Wtt, Fraude, witwasbestrijding, Wwft, Grondrechten, ICT, privacy, e-commerce | Tags: , , , | Plaats een reactie

Revision of beneficial ownership rules in AMLR | part 3 of Horrors of European legislation against crime (AML/CFT)

European beneficial ownership bureaucracy is a major headache for both entities that have to register (‘registering entities’) with the beneficial ownership register [1] (‘ubo-register’), as for ‘obliged entities’ [2] like banks and auditors.
Everyone involved with European beneficial ownership bureaucracy should prepare for revision of the rules through a new European AML/CFT [3] regulation: AMLR [4].

The European Commission, the Council and the Parliament still believe in the AML/CFT concepts, even though the failure of the system is apparent. The same applies to the illusion that – at the expense of undermining the data protection of the ‘beneficial owners’ (‘ubo’s’) registered – through the ubo-register crime can be countered.

Currently a draft AMLR is discussed and the amendments proposed by the LIBE and ECON committees are discussed as well. Some major changes regarding ubo/ubo-register are mentioned here.

Broadening the ubo-definition: ‘control through other means’ by having links with family members of directors/owners/controllers
In the draft AMLR ‘control through other means’ is explained in the recital (66):

Control through other means may include the right to appoint or remove more than half of the members of the board of the corporate entity; the ability to exert a significant influence on the decisions taken by the corporate entity; control through formal or informal agreements with owners, members or the corporate entities, as well as voting arrangements; links with family members of managers or directors or those owning or controlling the corporate entity; use of formal or informal nominee arrangements.

See article 42 draft AMLR.

The definition of ‘beneficial owner’ is is considerably widened by the inclusion of all family members of managers, directors, owners and controllers. This is improper and unnecessary and will lead to new gathering of personal data.

Broadening the ubo-definition / registration duty: lowering the percentage for the identification of beneficial ownership of legal entities to 5%
The Commission in article 63 draft AMLR proposes to present reports to the European Parliament and to the Council assessing the need and proportionality of lowering the percentage for the identification of beneficial ownership of legal entities that are registered in the ubo-register.
The ECON and LIBE committees do not want to wait for that. They propose to lower the threshold of control through ownership to 5% plus one of the shares or voting rights or other ownership interest, to be assessed on every level of ownership, read recital (65) in their draft:

(65) Detailed rules should be laid down to identify the beneficial owners of corporate and other legal entities and to harmonise definitions of beneficial ownership. While a specified percentage shareholding or ownership interest does not automatically determine the beneficial owners, it should be one factor among others to be taken into account. Control through ownership interest of 5% plus one of the shares or voting rights or other ownership interest should be assessed on every level of ownership, meaning that this threshold should apply to every link in the ownership structure and that every link in the ownership structure and the combination of them should be properly examined.

Proof of the ‘pseudo-ubo’
There are many registering entities that do not have a ‘real’ ubo (though the current definition is already ridiculously broad), e.g. many Dutch ‘stichtingen‘ in the nonprofit sector do not have a ‘real’ ubo.
When there is no ‘real’ ubo the senior officials of the entity are designated as ubo’s (‘pseudo-ubo’s’), even though they are registered with the trade register. The European lawmakers think that having a pseudo-ubo is extraordinary and require extra proof if there is such a pseudo-ubo. It leads extra bureaucracy (article 45 draft AMLR):

  • the corporate or other legal entities shall keep records of the actions taken in order to identify their beneficial owner(s);
  • the corporate or other legal entities shall provide (a) a statement, accompanied by a justification, that there is no beneficial owner or that the beneficial owner(s) could not be identified and verified and (b) details regarding the senior managing official(s).

The committees in their draft report add extra bureaucracy:

entities shall keep records of the actions taken in order to identify their beneficial owner(s), and provide additional information on a risk-sensitive basis, including resolutions of the board of directors and minutes of their meetings, partnership agreements, trust deeds, powers of attorney or other contractual agreements and documentation.

No explanation is given for these strange requirements.

The ubo who is a ‘high-net-worth individual’
The committees propose to qualify high-net-worth individuals as high risk, see recital 60a and article 36a of their draft. There will be many high-net-worth individuals, as the committees’ definition of such a person is (article 2(1)(27a) draft report):

a natural person who owns at least EUR 1 million or the equivalent in national currency in liquid financial assets

Certain high-net-worth ubo’s are super-high risk, according to the LIBE ECON proposal, that are those:

whose wealth derives prominently from the extraction of natural resources, from links with politically exposed persons or from the exploitation of monopolies

and they are added to Annex III of AMLR.

The definition of ‘politically exposed person’ will include siblings
The ubo may be a ‘politically exposed person’ (PEP) and is high risk then. The definition of PEP currently includes parents and children of the ‘primary’ PEP. According to the draft-report of the ECON LIBE committees siblings of a primary PEP also will be high risk.

Yearly verification of the ubo
According to the Commission’s draft obliged entities every year have to check the ubo-information (article 21 draft AMLR):

the obliged entity has a legal obligation in the course of the relevant calendar year to contact the customer for the purpose of reviewing any relevant information relating to the beneficial owner(s) or to comply with Council Directive 2011/16/EU

In article 44 (2) draft AMLR the Commission requires that registering entities shall update their ubo-information on an annual basis.

Non-EU legal entities to be registered in the ubo-register
Read the explanatory memorandum by the Commission, regarding AMLR:

Beneficial ownership information
The provisions on beneficial ownership information in the proposal build on those in current EU AML/CFT legislation, including the concept of beneficial ownership and the requirement for all corporate and other legal entities to obtain and hold adequate, accurate and current beneficial ownership information. More detailed rules are provided to identify the beneficial owner(s) of corporate and other legal entities, and a harmonised approach to the identification of beneficial ownership is laid down. With regard to express trusts and similar legal entities or arrangements, provisions are provided to ensure the consistent identification of beneficial owners across Member States when similar situations are faced, including an empowerment for a Commission implementing act. The proposal includes disclosure requirements for nominee shareholders and nominee directors, and introduces the obligations to register their beneficial ownership in the Union for non-EU legal entities that either enter into a business relationship with an EU obliged entity or acquire real estate in the Union.

See also article 48 draft AMLR and the fine-tuning in the committees’ draft.

It is interesting to see that if a non-EU legal entity is asking legal advice to which AMLR applies [5], this entity has to register its ubo’s in the country of the legal adviser. The same applies when a non-EU legal entity buys an art object in the EU with a value of EUR 10 000 or more [6].

Final remark
The European lawmakers love bureaucracy and will be applauded by compliance industry. Hopefully there is enough money in Europe to pay for compliance. Of course, it doesn’t help fight crime, but that’s okay. The most important thing is that lawyers and compliance industry can benefit.

Data protection damage must be accepted as a societal fact by the ‘beneficial owners’… or are they protected by GDPR against greedy European lawmakers?


Notes

[1] Please note that the ‘beneficial owner’ under European anti-money laundering legislation sometimes does not own anything and should be distinguished from the beneficial owner for tax purposes. For that reason the UK the first type of beneficial owners is referred to as ‘People with Significant Control’ (PSC). In Dutch: ‘uiteindelijk belanghebbende’, ‘ubo’.
[2] Companies that have to detect crime on behalf of the government and report suspicious transactions to that same government (‘obliged entities’).
[3] AML = anti-money laundering, CFT = countering terrorist financing. AML refers to all proceeds of crime, so in practice obliged entities have to conduct general crime detection.
[4] AMLR = Anti-Money Laundering Regulation, latest draft is to be found here. See also the draft report by ECON/LIBE proposing amendments to the draft AMLR.
[5] AML/CFT legislation only applies to certain activities of lawyers, including buying and selling of real property or business entities (article 3 (b) draft AMLR).
[6] Article 3 (i), (j) draft AMLR.


NB This article was published too early so the version sent by mail may differ from this version.


This is part 3 of the series Horrors of European legislation against crime (AML/CFT) that describes the European plans to fundamentally change AML/CFT legislation.

Geplaatst in English - posts in English on this blog, Europa, Financieel recht, onder meer Wft, Wtt, Fraude, witwasbestrijding, Wwft, Grondrechten, Ubo-register | Tags: , , , , , , | 1 reactie

Overige ubo-register nieuws uit het parlement | Wwft, witwasbestrijding

Zo even meldde ik het aannemen van een ubo-register motie. Enige andere ubo(-register) activiteit in het parlement:

Geplaatst in Financieel recht, onder meer Wft, Wtt, Fraude, witwasbestrijding, Wwft, Ubo-register | Tags: , | Plaats een reactie

Ubo-register motie aangenomen, geen sancties tot uitspraak Europees hof | Wwft, witwasbestrijding

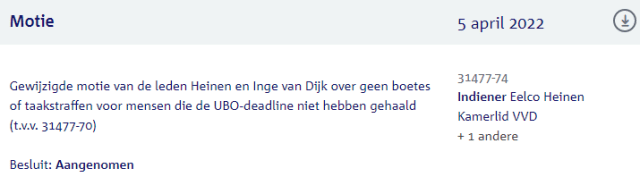
Op 5 april jl. zijn een aantal moties over witwasbestrijding aangenomen, onder meer de motie over uitstel van sancties tot na de uitspraak van het Europese hof:


Tekst:

overwegende dat het merendeel van de UBO’s op de deadline van 27 maart 2022 niet was geregistreerd bij de Kamer van Koophandel;

overwegende dat bij ondernemers zorgen zijn over de privacy van gezins- en familieleden;

overwegende dat het Hof van Justitie van de Europese Unie de komende maanden uitspraak doet over de publieke toegankelijkheid van gegevens in het UBO-register en dit kan leiden tot noodzakelijke wetswijzigingen;

verzoekt de regering tot deze uitspraak geen boetes of taakstraffen op te leggen en handhaving alleen risico gebaseerd plaats te laten vinden gericht op significante risico’s voor witwassen of andere strafbare activiteiten;

verzoekt de regering tevens de uitspraak van het Hof van Justitie van de Europese Unie onverkort op te volgen,


Stemverdeling:

Geplaatst in Financieel recht, onder meer Wft, Wtt, Fraude, witwasbestrijding, Wwft, Grondrechten, ICT, privacy, e-commerce, Ubo-register | Tags: , | 1 reactie

Renseigneringsplicht digitale platformen: wetsvoorstel naar het parlement | databeschermingsrisico’s nemen toe

Eerder schreef ik dat de databeschermingsrisico’s van burgers toenemen vanwege de Europees voorgeschreven renseigneringsplicht van digitale platformen ten behoeve van de belastingheffing, zie ook mijn bericht uit 2020.

In een nieuwsbericht met de verhullende en onjuiste titel “Meer transparantie over inkomsten digitale platformen” kondigt het kabinet aan dat het wetsvoorstel is aangeboden aan de Tweede Kamer.

Voor degenen die gebruik maken van dit soort platformen is alertheid geboden, nu de platformen net als werkgevers zeer veel persoonsgegevens en andere vertrouwelijke gegevens moeten verzamelen (meer dan nu), die zij aan de overheid moeten verschaffen en die zij mogelijk ook voor andere doelen zullen gaan gebruiken, ook al is het officieel verboden. Nu de handhaving van de AVG en andere relevante wetgeving (zoals inzake cybersecurity) te wensen over laat, is het belangrijk goed na te gaan of het platform betrouwbaar is. Een lastige opdracht.

Het nieuwsbericht:

Meer transparantie over inkomsten digitale platformen
Nieuwsbericht | 23-03-2022 | 17:17

Vandaag is het wetsvoorstel transparantie over inkomsten digitale platformen (ook wel DAC7) aangeboden aan de Tweede Kamer. Met dit wetsvoorstel worden digitale platformen vanaf 1 januari 2023 verplicht jaarlijks informatie aan te leveren aan de Belastingdienst over verkopers die via hun platformen geld verdienen. Deze informatie wordt automatisch uitgewisseld met de belastingautoriteiten van de EU-lidstaten voor wie deze informatie van belang is. Zo wordt voorkomen dat mensen (onbedoeld) belasting kunnen ontwijken via deze platformen.
Met het wetsvoorstel komt er meer transparantie over inkomsten die inwoners van de Europese Unie behalen via de digitale platformen. Dit vermindert de kans dat belastingplichtigen deze inkomsten niet (volledig) opgeven en zorgt daardoor voor een eerlijkere belastingheffing. Ook wordt oneerlijke concurrentie met traditionele (niet digitale) bedrijven op deze manier tegengegaan. Als je bijvoorbeeld via een digitaal platform je huis verhuurt, of als taxichauffeur via een platform je diensten aanbiedt, dan moet dit platform in de toekomst informatie hierover -bijvoorbeeld over de behaalde inkomsten – doorgeven aan de Belastingdienst.

Een digitaal platform levert de informatie aan bij één EU-lidstaat. Om de belastingautoriteiten van alle EU-lidstaten de informatie te bezorgen die zij nodig hebben om de verschuldigde belastingen correct vast te stellen, wordt deze informatie vervolgens via een centraal beveiligd systeem van de Europese Unie uitgewisseld met de EU-lidstaten die hierbij belang hebben.
Naast deze verplichting bevat het wetsvoorstel ook een aantal wijzigingen die niet specifiek gericht zijn op digitale platformen, maar de manier van gegevensuitwisseling tussen EU-lidstaten verbeteren. Het gaat hierbij bijvoorbeeld over rechtsbescherming van belastingplichtigen bij gezamenlijke onderzoeken door meerdere EU-lidstaten en gegevensbescherming bij een datalek.

Met dit wetsvoorstel wordt de EU-richtlijn transparantie inzake inkomsten via de digitale platformeconomie en overige aanpassingen geïmplementeerd in de Nederlandse wetgeving. Ook de andere EU-lidstaten zullen deze richtlijn op vergelijkbare wijze implementeren.


Aanvulling 6 april 2022, 11:45 uur
Een belastingadviseur reageerde per e-mail op dit artikel,

Let er wel op dat de verwerking van deze gegevens gebeurt met een ‘geheimhouder’. De verwerking van de persoonsgegevens is nu wel gebaseerd op een uitdrukkelijke wettelijke bepaling, zodat dit conform art 6 AVG gebeurt. Zonder uitdrukkelijke wettelijke bepaling zou je kunnen twijfelen aan de evenredigheid van het verwerken van zoveel gegevens. Zie ook arrest SS Sia, C-175/20 (…). Als de DAC 7 richtlijn in strijd komt met de beginselen van de AVG, moet er een balans gevonden worden. Het is namelijk niet vanzelfsprekend dat de verkoop van goederen via een platform leidt tot belastbare inkomsten. De populatie waarvan gegevens verzameld worden kan dus veel te groot zijn voor belastingdoeleinden. Maar ik denk niet dat de DAC 7 en wetsontwerp 36063 daarom in strijd komen met het VEU en VWEU en Handvest.
De verkopen gedurende 2023 worden voor het eerst per 1 jan 2014 doorgegeven.

Mijn probleem is niet met de wettelijke grondslag, die zal er wel zijn, maar de cybersecurity / databescherming, het voorkomen van rondslingeren van persoonsgegevens.
Op mijn vraag wie er onder deze wet vallen antwoordt de belastingadviseur:

Marktplaats zeker en E-Bay ook. Fiscus zit nu ook al achter marktplaats aan, omdat zij ook commerciële partijen (ondernemers) faciliteren.
Youtube weet ik niet, maar ik denk het wel, zo ook Instagram en al die influencers die betaald worden.

Dus dat gaat spannend worden als persoonsgegevens aan Amerikaanse datagraaiers moeten worden afgegeven.

Geplaatst in Belastingrecht, Financieel recht, onder meer Wft, Wtt, Fraude, witwasbestrijding, Wwft, ICT, privacy, e-commerce | Tags: , , , | Plaats een reactie

New data retention judgment by the Grand Chamber of the European Court of Justice

Today a new data retention judgment by the Grand Chamber of the European Court of Justice was made public. The court ruled amongst others that the Charter precludes “legislative measures which, as a preventive measure for the purposes of combating serious crime and preventing serious threats to public security, provide for the general and indiscriminate retention of traffic and location data“.

The decision:

On those grounds, the Court (Grand Chamber) hereby rules:

1. Article 15(1) of Directive 2002/58/EC of the European Parliament and of the Council of 12 July 2002 concerning the processing of personal data and the protection of privacy in the electronic communications sector (Directive on privacy and electronic communications), as amended by Directive 2009/136/EC of the European Parliament and of the Council of 25 November 2009, read in the light of Articles 7, 8 and 11 and Article 52(1) of the Charter of Fundamental Rights of the European Union, must be interpreted as precluding legislative measures which, as a preventive measure for the purposes of combating serious crime and preventing serious threats to public security, provide for the general and indiscriminate retention of traffic and location data. However, that Article 15(1), read in the light of Articles 7, 8, 11 and 52(1) of the Charter of Fundamental Rights, does not preclude legislative measures that provide, for the purposes of safeguarding national security, combating serious crime and preventing serious threats to public security, for
– the targeted retention of traffic and location data which is limited, on the basis of objective and non-discriminatory factors, according to the categories of persons concerned or using a geographical criterion, for a period that is limited in time to what is strictly necessary, but which may be extended;
– the general and indiscriminate retention of IP addresses assigned to the source of an internet connection for a period that is limited in time to what is strictly necessary;
– the general and indiscriminate retention of data relating to the civil identity of users of electronic communications systems; and
– recourse to an instruction requiring providers of electronic communications services, by means of a decision of the competent authority that is subject to effective judicial review, to undertake, for a specified period of time, the expedited retention of traffic and location data in the possession of those service providers,
provided that those measures ensure, by means of clear and precise rules, that the retention of data at issue is subject to compliance with the applicable substantive and procedural conditions and that the persons concerned have effective safeguards against the risks of abuse.

2. Article 15(1) of Directive 2002/58, as amended by Directive 2009/136, read in the light of Articles 7, 8 and 11 and Article 52(1) of the Charter of Fundamental Rights, must be interpreted as precluding national legislation pursuant to which the centralised processing of requests for access to data, which have been retained by providers of electronic communications services, issued by the police in the context of the investigation or prosecution of serious criminal offences, is the responsibility of a police officer, who is assisted by a unit established within the police service which has a degree of autonomy in the exercise of its duties, and whose decisions may subsequently be subject to judicial review.

3. EU law must be interpreted as precluding a national court from limiting the temporal effects of a declaration of invalidity which it is bound to make, under national law, with respect to national legislation imposing on providers of electronic communications services the general and indiscriminate retention of traffic and location data, owing to the incompatibility of that legislation with Article 15(1) of Directive 2002/58, as amended by Directive 2009/136, read in the light of the Charter of Fundamental Rights. The admissibility of evidence obtained by means of such retention is, in accordance with the principle of procedural autonomy of the Member States, a matter for national law, subject to compliance, inter alia, with the principles of equivalence and effectiveness.


More information:

Geplaatst in English - posts in English on this blog, Europa, Grondrechten, Strafrecht | Tags: , , , | 1 reactie

Energiebedrijf lapt databeschermingswet AVG aan zijn laars en krijgt van de rechter op zijn kop

Energiebedrijven zijn zwakke organisaties als het om de omgang met persoonsgegevens gaat, zodat het verbazingwekkend is dat de overheid het goed vindt dat zij ‘slimme’ meters mogen beheren [*].

In 2016 schreef ik over het gigantische datalek dat zich destijds bij de energiebedrijven heeft voorgedaan en in 2019 over de handel in persoonsgegevens waaraan deze bedrijven zich illegaal schuldig hebben gemaakt.

Het is geen verrassing dat energiebedrijven met de rechter te maken krijgen op het gebied van bescherming van persoonsgegevens. De Rechtbank Gelderland oordeelde op 17 januari 2022 dat het energiebedrijf Zakelijk Energie Beheer B.V. (‘ZEB’) te Amsterdam laakbaar had gehandeld door de weigering te voldoen aan verzoeken die een door ZEB aangeschreven persoon (‘X’) deed.

Achtergrond
ZEB had via illegale weg persoonsgegevens van X verkregen – via advertentie- of marketingbedrijven – en had X op 19 maart 2021 gebeld. Daar was X niet blij mee, die dezelfde dag ZEB diverse AVG-verzoeken deed. X wilde weten welke persoonsgegevens ZEB had, wie zijn gegevens aan ZEB had verschaft en aan wie ZEB de gegevens had doorgegeven. ZEB beriep zich er op dat zij de persoonsgegevens van X zou mogen verwerken op grond van ‘gerechtvaardigd belang’ (een bekende AVG-dooddoener voor ongevraagde marketingactiviteiten) en weigerde medewerking.

Procedure
Vervolgens spant X een procedure aan die hij wint in een voor hem gunstige uitspraak (‘beschikking’). De Rechtbank beveelt ZEB:

  • om binnen veertien dagen na de beschikking aan X inzage te geven in de van hem verwerkte persoonsgegevens, waaronder de verwerkingsdoeleinden, middels het verstrekken van een compleet overzicht van alle van hem verzamelde persoonsgegevens per gerechtvaardigd belang en per verwerking met daarbij genoemd de verwerkers die namens ZEB zijn persoonsgegevens hebben verwerkt,
  • om binnen veertien dagen na de beschikking X de informatie te verstrekken bedoeld in de leden 1 en 2 van art. 14 AVG (allerlei verplichte gegevens die verstrekt moeten worden als gegevens van derden worden betrokken),
  • om binnen veertien dagen na deze beschikking aan X een lijst te verstrekken van alle verwerkers en bedrijven met wie ZEB zijn persoonsgegevens heeft gedeeld en van wie zij de persoonsgegevens van X heeft ontvangen, met daarbij vermeld op basis van welke grondslag de persoonsgegevens zijn ontvangen,
  • om binnen veertien dagen nadat zij aan de hiervoor vermelde bevelen heeft voldaan de persoonsgegevens van X te wissen.

Bij niet-nakoming is ZEB een dwangsom verschuldigd en verder wordt het energiebedrijf in de kosten veroordeeld. Deze uitspraak vormt een flinke waarschuwing voor iedereen die illegaal verkregen persoonsgegevens van advertentie- en marketingbedrijven gebruikt.

Het zou goed zijn al iedereen die met dit soort praktijken te maken krijgt, achter de overtreders van de AVG aangaat, zoals degene die ik met ‘X’ heb aangeduid in deze zaak heeft gedaan.


Noot

[*] Slimme meters leveren cybersecurity risico’s voor burgers op.
Wellicht dat de zwakke financiële positie van energiebedrijven bijdraagt aan de desinteresse voor databescherming, zie over die financiële situatie het recente bericht van de ACM, ACM stelt vooruitlopend op nieuwe wetgeving extra eisen aan energieleveranciers (23 maart 2022), waarover veel is geschreven, onder meer door NRC (1, 2), AD EN Radar. ACM komt zeer laat in actie want het is al vele jaren bekend dat energiebedrijven financieel zwak zijn, zie mijn eerdere artikel. Het leveren van deze primaire producten hoort niet thuis bij private bedrijven.

Geplaatst in ICT, privacy, e-commerce | Tags: , | Plaats een reactie

BKR-registratie dient te worden verwijderd | Rechtbank Amsterdam 9 december 2021

In mijn serie BKR-uitspraken hoort ook de uitspraak van Rechtbank Amsterdam van 9 december 2021 in de zaak van Hoist Finance AB (‘Hoist’).
De Rechtbank oordeelde dat de klanten van Hoist de getroffen betalingsregeling steeds zijn nagekomen, het volledige kredietbedrag en daarnaast rente hebben terugbetaald en dat hun financiële situatie stabiel is, zodat het verzoek om doorhaling van de BKR-registratie wordt toegewezen.

Eerder schreef ik op dit blog al over de BKR-registratie:

Geplaatst in Financieel recht, onder meer Wft, Wtt | Tags: , , , , | Plaats een reactie

European Banking Guide for Nonprofits | ECNL, AML, CFT

The European Center For Not-for-Profit Law (ECNL) has seen that civil society organisations (CSOs) increasingly encounter difficulties in opening and maintaining bank accounts, due to the detrimental effects of legislation in regard of anti-money laundering (AML) and combatting terrorist financiering (CFT), requiring banks to carry out expensive customer due diligence. This is caused by incorrect risk assessments by the authorities on the nonprofit and by risk-averse behaviour of banks (‘de-risking’).

ECNL together with PILnet has launched a series of overviews of banking conditions in European countries.  ECNL writes on its website:

These overviews aim to support CSOs that wish to open a bank account in the selected countries or compare conditions between these countries. It aims to help CSOs navigate through the organizational banking requirements which are becoming increasingly complex. The countries and issues in these overviews have been selected based on requests lodged to our organizations by national and international partners.

New profiles will be uploaded on a rolling basis.

Our overviews provide information on the following issues:

1. REQUIREMENTS FOR OPENING AN ORGANIZATIONAL BANK ACCOUNT, INCLUDING:

  • Whether physical presence of a legal representative is required;
  • Specific requirements related to organization’s internal operation, such min./max. annual turnover, nationality of statutory representatives etc.;
  • Who is authorized to open organizational bank account;
  • General information about the process, including timelines.

2. BANKING ACTIVITIES, INCLUDING:

  • Customer due diligence requirements;
  • Monitoring criteria for suspicious transactions;
  • Limitations to bank transactions and transfers to certain jurisdictions.

3. OBLIGATIONS AND REPORTING REQUIREMENTS:

  • Reporting to regulatory and public authorities by banks;
  • Protection of privacy of clients’ information;
  • Reporting to public authorities about civil society banking.
Geplaatst in English - posts in English on this blog, Europa, Financieel recht, onder meer Wft, Wtt, Fraude, witwasbestrijding, Wwft | Tags: , , , , , , | Plaats een reactie

Wetsvoorstel over verkorten betaaltermijnen aangenomen

Op 17 maart verscheen het bericht dat het wetsvoorstel inzake verkorting van betalingstermijnen is aangenomen. Of het enige effect gaat sorteren voor het mkb mag worden betwijfeld, nu het kabinet niet bereid is tijdige betaling op een betere manier af te dwingen, bijvoorbeeld doordat dit onderdeel wordt van de accountantscontrole bij grote ondernemingen, zie wat ik er eerder over schreef, onder meer dit.

Nieuwsbericht:

Wetsvoorstel over verkorten betaaltermijnen aangenomen
Nieuwsbericht | 17-03-2022 | 16:42

Het wetsvoorstel om de maximale wettelijke betaaltermijnen van het grootbedrijf aan het midden- en klein bedrijf (mkb) te verkorten van 60 naar 30 dagen is dinsdag aangenomen door de Tweede Kamer. Hiermee wordt de huidige toegestane betaaltermijn gehalveerd en gelijkgesteld aan die van de overheid.

Mkb’ers beter beschermd
Kleine en middelgrote ondernemers die aan het grootbedrijf leveren, gaven in onderzoeken aan dat er steeds later wordt betaald in plaats van eerder. Ook bleek dat de betaaltermijn regelmatig door het grootbedrijf wordt bepaald en in sommige gevallen zelfs eenzijdig wordt verlengd. Dit laatste is sinds de coronacrisis steeds vaker het geval waardoor kleinere ondernemers extra in de problemen kunnen komen.

Mkb’ers beschikken over het algemeen over kleinere reserves, late betalingen hebben een negatieve invloed op de kaspositie en daarmee op de levensvatbaarheid van mkb-ondernemingen. Het verkorten van de betaaltermijn kan hierbij het verschil maken. Met dit aangenomen wetsvoorstel worden mkb’ers beter beschermd.

Melding maken van te late betalingen
Ondernemers in het midden- en kleinbedrijf (mkb) kunnen melding maken van te late betalingen. Dit kan volledig anoniem bij het tijdelijke Meldpunt Achterstallige Betalingen, dat de Autoriteit Consument en Markt (ACM) in januari 2021 heeft opgezet. Dit meldpunt blijft langer geopend, ondernemers kunnen tot 26 januari 2023 hun melding doen.


Aanvulling 18 mei 2022
Het besluit met de inwerkingtredingsdatum is in het Staatsblad gepubliceerd. De wetswijziging treedt op 1 juli 2022 in werking. Met ingang van die datum moeten mkb’ers voortaan binnen dertig dagen hun rekeningen betaald krijgen door het grootbedrijf.

Geplaatst in Contractenrecht, privaatrecht algemeen, Financieel recht, onder meer Wft, Wtt | Tags: , , | Plaats een reactie
